

Ernst has just posted his code for an ssl interceptor he just created. It looks awesome so take a look for yourself.
Blog
Recent Entries
Inherited a CFML Application With Few Tests? Here’s Where to Start!
You need to change an application that has been running for years.
It might be a ColdFusion customer portal, a Lucee application supporting internal operations, or a CFML system your team is preparing to modernize. People depend on it, but some of its behavior lives in old tickets, scattered documentation, and the memory of whoever has supported it longest.
Now a release is approaching. You know more testing would help. The difficult part is deciding where to begin without putting every other priority on hold.
Start with one important workflow and build evidence around what it needs to do.
Maria Jose Herrera


Maria Jose Herrera
October
27,
2026
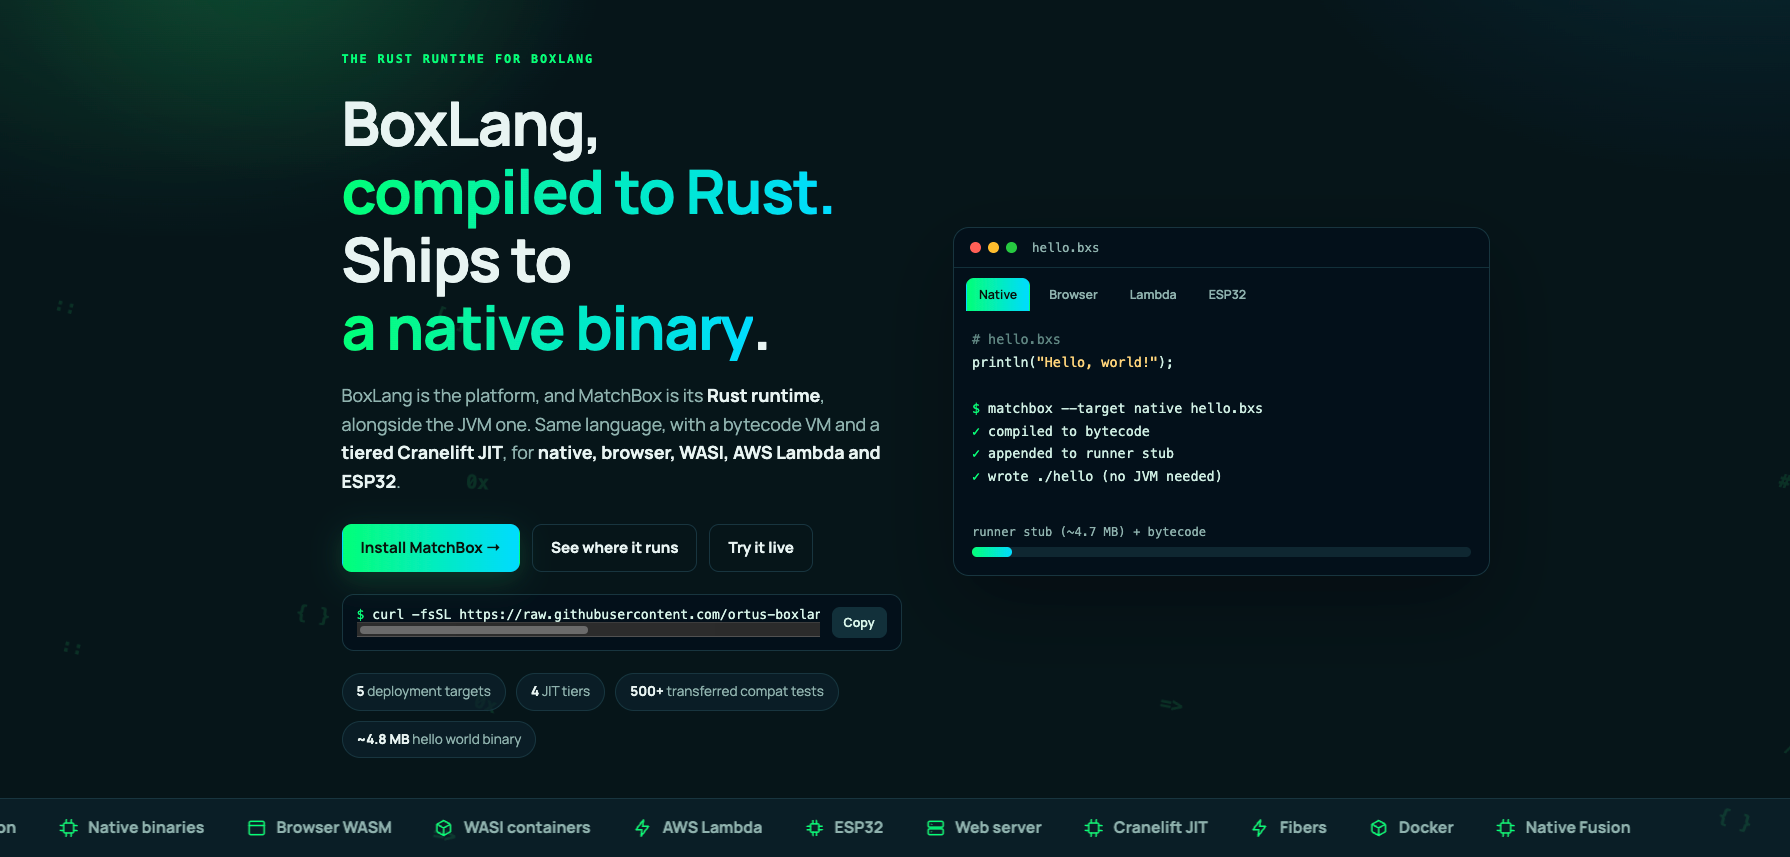
MatchBox 0.12: One Language, Every Runtime, Now with a Live Playground and a Course
Ortus Solutions today announces MatchBox 0.12.0, the Rust runtime for BoxLang, alongside the launch of matchbox.boxlang.io: a new website with a live in-browser playground, a ten-lesson course, and complete online docs. The release also brings a more capable JIT, prebuilt native modules, a richer web runtime, and a long list of BoxLang compatibility fixes.
Luis Majano


Luis Majano
October
27,
2026
Your ColdFusion Upgrade Passed. Did Your Business Workflows?
The server restarted. The administrator shows the expected version. Your homepage loads, and a few familiar screens look fine.
Would you tell the business the upgrade is complete?
Consider an illustrative scenario: a customer submits an order after an upgrade. The application saves it and displays a confirmation page. But the confirmation email never arrives, and the scheduled process that sends the order to fulfillment has not completed.
From the browser, the transaction...
Maria Jose Herrera
Maria Jose Herrera
October
22,
2026
Add Your Comment
(4)
Jan 19, 2008 23:50:35 UTC
by Rob Gonda
It's missing some functionality ... how does it know which event has to be secured? It should secure only specific events, and force unsecured requests for the rest. something like
if not isSsl and requireSll then cflocate to https
if isSsl and not requireSll then cflocate to http
Jan 19, 2008 23:54:53 UTC
by Luis Majano
That is up to Ernst, but I think its a good start.
Jan 21, 2008 16:01:48 UTC
by Ernst van der Linden
Rob you're right. We could implement that. Just make a list of allowed events without SSL as a property in interceptor xml definition and then check with event.getCurrentEvent() if we need SSL.
I will take a look and keep you informed.
Jan 21, 2008 17:47:57 UTC
by Ernst van der Linden
Rob, I made in new blog entry. The SSL interceptor now supports SSL for specific events.
Comments are welcome!